Stop Losing Deals to Security Questionnaires and Compliance Gaps
GRC experts helping growing companies get SOC 2, HIPAA, and ISO 27001 ready — without hiring a full-time compliance team.
COMPLIANCE, TPRM & SECURITY without the Team
Securing Small & Growing Companies
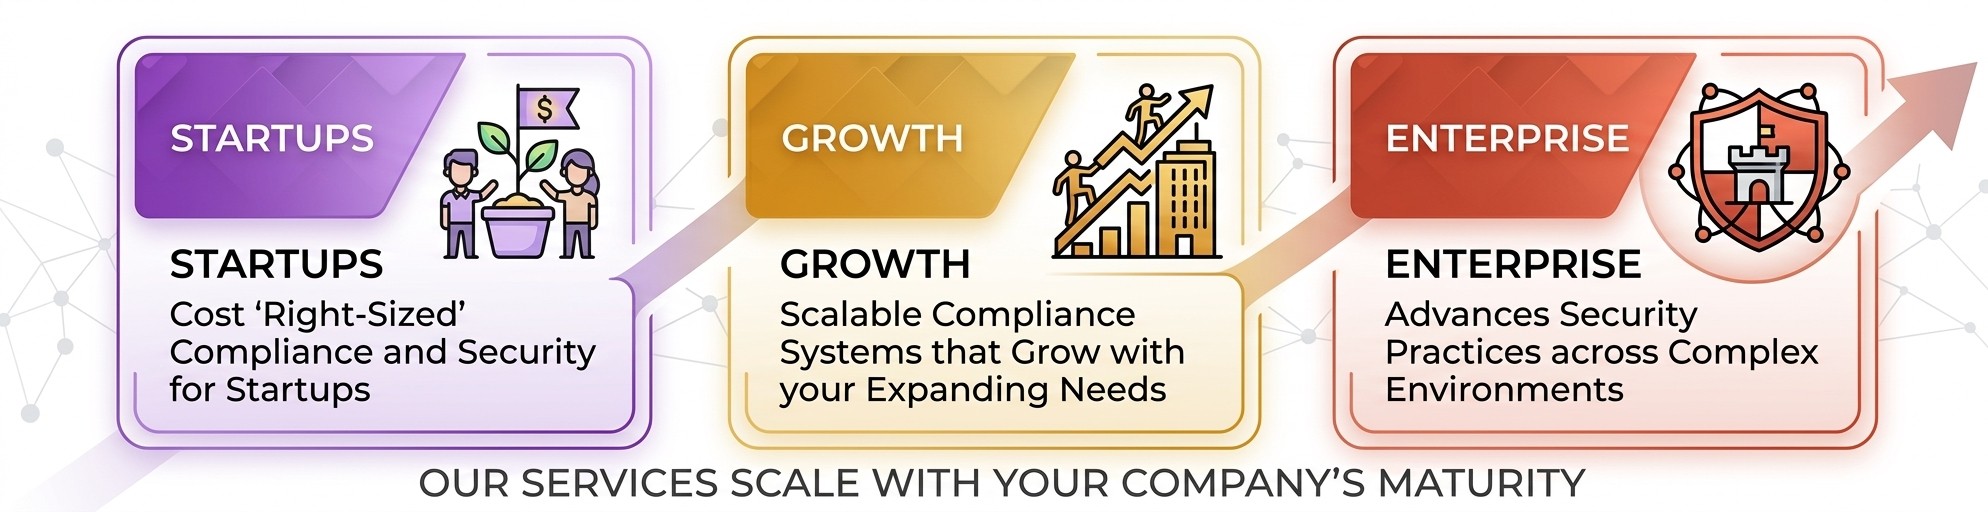
Ongoing Compliance, TPRM & vCISO as a Service or One Time Project-Based Consulting to help you meet customer, regulatory and contractual security requirements.
We Make GRC Our Passion
So You Don't Have To ™
PROJECT CONSULTING
Expert help for specific projects.
- SOC 2 / PCI / NIST readiness
- ISO 27001 readiness
- vCISO
- Cybersecurity Guidance
- Security Assessments
- Compliance Assessments
- Regulatory Assessments
- NYDFS / CCPA / GDPR / SOX
- Customer security requirements
COMPLIANCE as a SERVICE
Customized to work as your team
- SOC 2 readiness
- ISO 27001 readiness
- HIPAA
- PCI DSS
- NIST CSF / NIST 800-53
- CIS Controls
- GDPR / CCPA
- NYDFS
- SOX
- Vendor/customer security requirements
TPRM as a SERVICE
Customized to work as your team
- Vendor inventory and risk classification
- Vendor security assessments
- SIG / CAIQ questionnaires
- SOC 2 / ISO 27001 evidence
- Vendor risk scoring
- Remediation tracking
- Annual reassessments
- Ongoing vendor monitoring
Compliance
Certifications
Turnkey framework compliance for SOC2, PCI, HIPAA, ISO, CMMC
Audit Mgmt
Quick audit expert preparation and gap analysis
Policy Development
Build and maintain policies guiding company trust
Security
Virtual CISO
Full-service security & strategy support at a fractional cost
Cloud Security Architect
Agile secure cloud infrastructure right fitting your goals
Access & ID Control
Limit risk on need-to-have identity access priciples
Risk Management
Vendor Mgmt as Service
Full-service vendor mgmt & vetting without the internal team costs
Manage 3rd Party Risk
Reduce exposure through ongoing vendor risk assessments
Risk Gap Remediation
Identify weaknesses and implement practical mitigation strategies
M&A Security
Assess Acquisition Risk
Identify security, compliance, and risks before the deal
Fast Due Diligence
Quickly uncover critical technology, security, and compliance gaps
M&A Decisions
Turn technology and security findings into actionable deal insights
Quickly Build a Compliance & TPRM Program for 50% LESS
Stop stressing over customer security questionnaires and regulatory audits
Companies we worked for and with
Secure. Comply. Thrive. Grow... Quickly
Security and compliance aren’t just checkboxes—they’re competitive advantages.
"We help you quickly build resilient systems and meet regulatory demands with innovation while controlling costs."
Founder & CISO, Thomas S. Donohue, MS, MBA
904.793.3764
FREE 30 minute Compliance & Security Readiness Call
Get expert guidance with a FREE CONSULTATION. Contact us to assess your cybersecurity and compliance needs and discover practical steps to reduce risk and strengthen your defenses.
So You Don't Have To ™
904.793.3764
Tampa, Jacksonville & NYC